


On the evening of October 29, the largest cryptocurrency theft in history occurred at Binance. The hot wallet of the world’s largest cryptocurrency exchange was drained of 233 million XRP within ten minutes, followed by 18,270 Bitcoin and more than 200,000 Ether, across ten blockchains. On the evening of November 3, Binance released its first completePreliminary report, laying out the full story of this attack. The answer is somewhat ironic: it began with a fake interview. According to the official report, this was an attack prepared over several months and carried out in multiple stages; the attackers combined fake job interviews, malware downloads, compromised internal AI tools, endpoint compromise, and advanced transaction authorization techniques. The report cites the latest FBI information and states that North Korea is responsible for the incident. On-chain analytics firm TRM Labs also attributed the attack with high confidence to the North Korean elite hacking group TraderTraitor, at about four times the scale of the February 2025 Bybit $1.5 billion case.
A fake interview allowed North Korean hackers to steal $6.3 billion from Binance.
Binance refers to the three engineers involved as A, B, and C, and the entire attack chain had been set up since June.
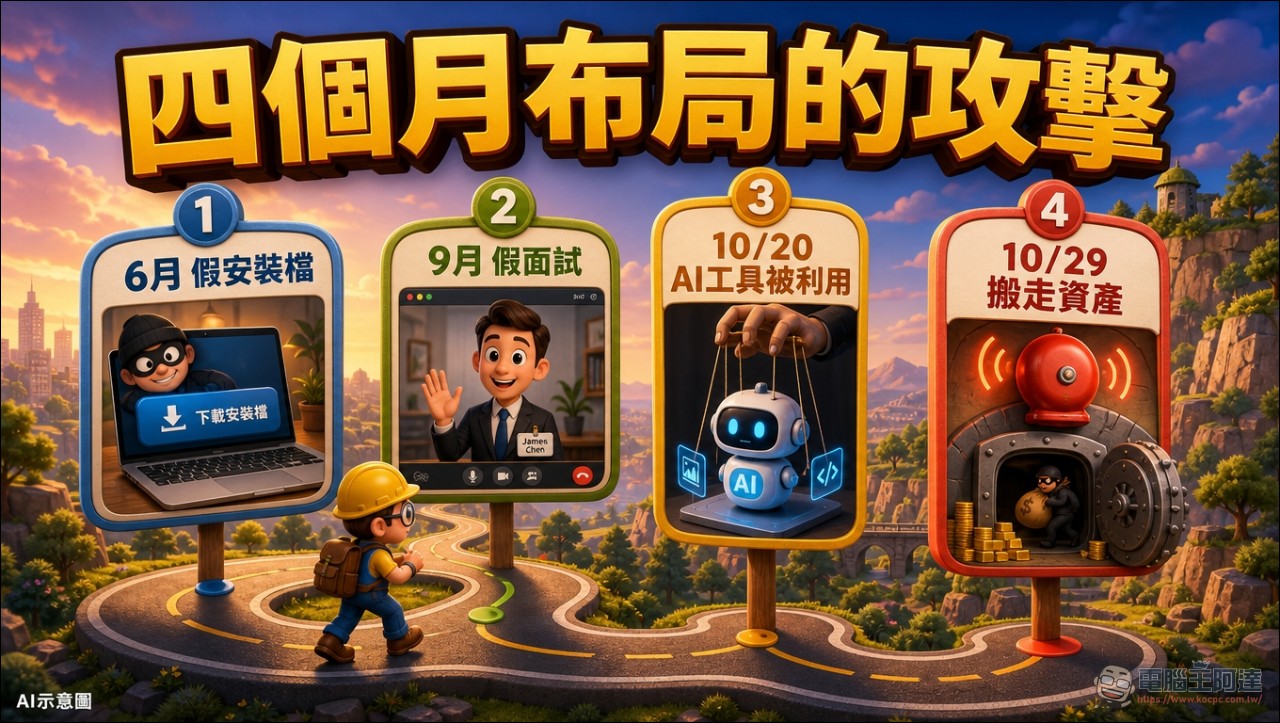
In June, a supply chain attack.Wallet DevOps engineer A wanted to install a popular AI coding tool, found it through a search engine, and downloaded a tampered Homebrew installer. Binance’s security team detected the anomaly, replaced his computer, and rotated all related credentials. The official report acknowledged that although this step stopped it, engineer A’s role and the list of his colleagues on the wallet infrastructure team were still exposed to the hackers as a result.
The report also disclosed a figure: since 2026, Binance’s security team has detected and blocked 57 cyberattacks suspected to be linked to North Korea. Common tactics include fake interviews, malware disguised as popular developer tools, trojanized packages and browser extensions, and fake video conferencing applications. This incident is a more sophisticated version of this attack vector.
September: social engineering.Software engineer B was contacted on a legitimate job platform by someone claiming to be a “Project Director.” B’s profile page on the platform lists work experience at Binance.
The fake project director arranged two rounds of interviews. The first was a live video interview with an “HR representative,” who even shared their social media account, which contained personal photos and videos posted on the platform, to build trust. The Binance report specifically noted that this was more deceptive than social engineering tactics seen in the past. The second round was moved to a popular social chat app, and the interviewer claimed to be the CEO of a fictitious company.
At the end of the interview, B was asked to download an “assignment” to his work computer. The official original text clearly states: “Engineer B was instructed to download an ‘assignment’ containing a repository of malicious code to his work computer. The repository contained malicious code that would execute during the installation and setup process, triggering a series of unauthorized activities.”
That malware was a zero-day (0-day) sample, and endpoint protection tools did not detect it at the time. One of the things it did was replace legitimate development tool components on the computer with malicious versions, which were used to execute commands and connect back to an external server controlled by the attacker. The attacker also deliberately erased traces of the intrusion, making detection and subsequent investigation more difficult.
Binance listed the specific file operation sequence in the report: create /opt/homebrew/Cellar/pyenv/2.8.0/libexec/pyenv_, modify it to 3,414 bytes, delete the legitimate 3,344-byte pyenv, then rename the malicious version to pyenv and overwrite it back, and finally delete it. /opt/homebrew/bin/pyenv and create a new symbolic link and launch zsh. pyenv is a tool for managing multiple Python versions and environments, and developers use it every day.
AI tools have become a springboard.
October 20.The attacker used Engineer B’s compromised computer to gain control of the computers of Engineer A and another wallet software engineer, C, through an internal Binance AI tool. They then discovered that a token with container deployment permissions was stored on Engineer A’s computer.
The official report did not explain the purpose of this internal AI tool, nor did it detail the specific ways it was exploited. When Chain News compiled the information, it specifically highlighted this gap. This part was classified as technical details to be kept confidential, on the grounds of preventing malicious actors from using them to plan the next attack.
October 29, 17:15 to 19:56.The attacker logged into Engineer C’s computer and used credentials obtained from Engineer A to deploy a container, triggering a malicious script to launch an attack.[2]In Taiwan time, this is approximately 1:15 a.m. to 3:56 a.m. on the 30th.
The access obtained was to Binance’s internal wallet signing service, allowing transactions to be issued directly while bypassing the normal withdrawal process.
Moved 6.3 billion in just over twenty minutes.
From 20:05 to 20:09 UTC, which is 4:05 a.m. to 4:09 a.m. Taipei time on the 30th, five Binance hot wallets transferred 233 million XRP to the attacker’s address, leaving only the minimum balance in each wallet. Hot wallets on Solana and Optimism subsequently transferred out approximately 970,000 SOL and 44.2 million OP.
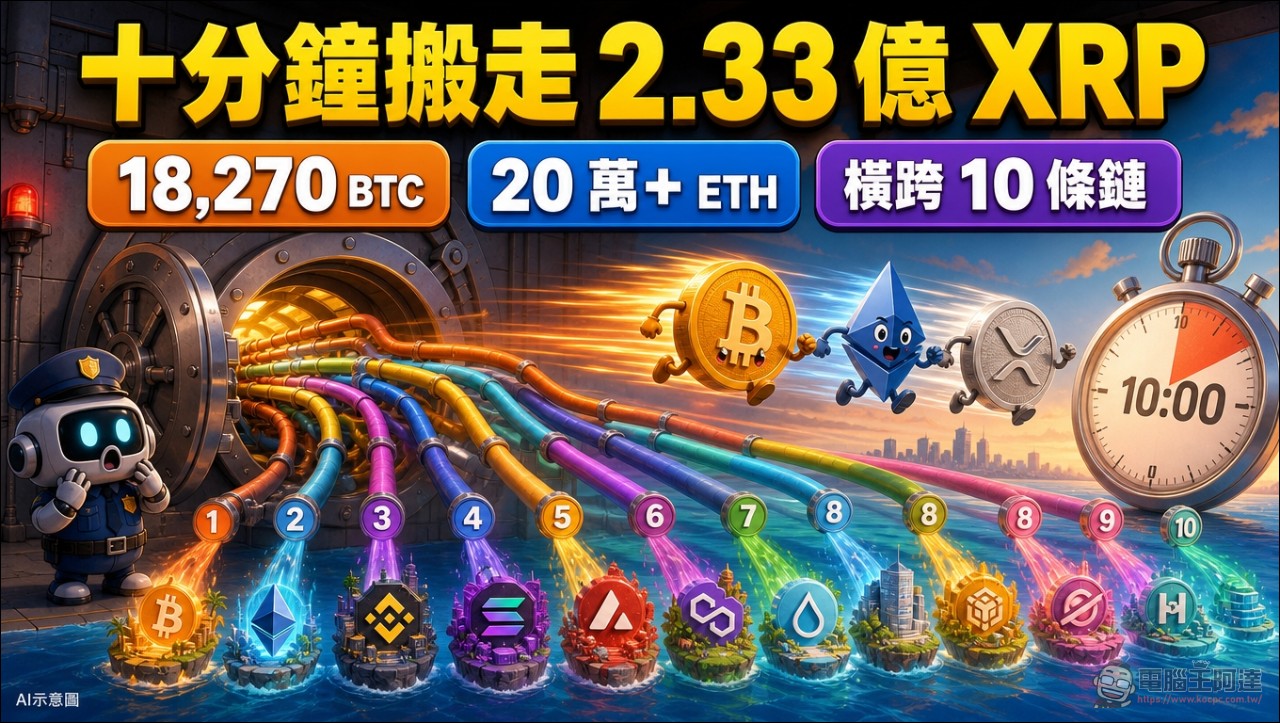
At 20:20 UTC, Binance received an internal alert about a large transfer and began investigating. At the same time, a Bitcoin hot wallet sent out 18,270 BTC. TRM Labs recorded that the funds were split within the same block into chunks of 1,000 and 100 BTC; this technique, known as a “peel chain,” makes the funds harder to trace.
The loss amounts on each chain are tracked transaction by transaction by TRM Labs:
- Ethereum: Approximately US$3.79 billion, including 200,630 ETH and 185 other tokens
- Bitcoin: 18,270 coins, approximately $1.47 billion
- Tron: 612.7 million USDT and 46.4 million TRX, approximately $628 million
- XRP Ledger233 million XRP, approximately $296 million
- Solana: 970,000 SOL, approximately US$96 million
- Arbitrum、Optimism、Base: Total approximately USD 39 million
- Avalanche: Approximately US$28 million;Polygon: Approximately $10 million USD
Why didn’t suspending withdrawals stop it?
The most critical technical part of the attack is EIP-7702. Binance’s official description is quite clear: the attacker sent 50 signed transactions, manipulated the account’s nonce, and created malicious delegation authorizations. Once these authorizations are written on-chain, the malicious authorizations can operate independently of Binance’s withdrawal infrastructure; pausing withdrawals or shutting down hot wallet services will not cause them to automatically expire.
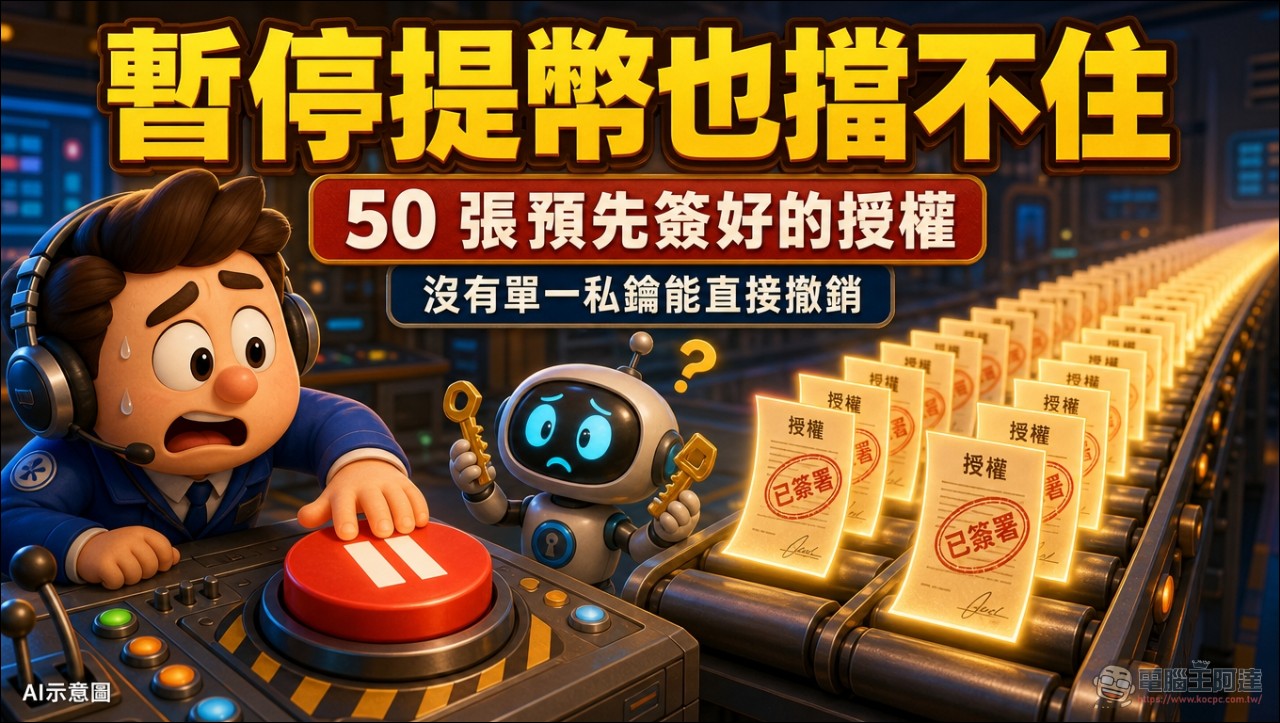
TRM Labs has filled in the operating principle of EIP-7702, a mechanism introduced by Ethereum’s Pectra upgrade in May 2025 that allows an ordinary wallet to sign an authorization and then hand control of its behavior to a smart contract. Each wallet has an incrementing transaction counter, and an authorization is valid only at a specific counter value. Binance hot wallets handle steady withdrawal traffic, so the counter keeps advancing; an attacker prepares 50 signatures for consecutive counter values at once, ensuring that at least one is still valid when the transaction executes.
As a result, three minutes and 24 seconds after the delegation approval, the attacker instructed the wallet to transfer out its entire balance, moving 167,464 ETH and 63 tokens in a single transaction, including 1.615 billion USDT. The approval remained in place, and newly arriving funds were subsequently swept six more times, at 20:41, 20:59, 21:04, 21:44, 22:39, and 23:56 UTC.
Revoking the authorization has a second layer of trouble. Binance said these hot wallets use multi-party computation (MPC), and no single private key can directly sign the revocation transaction, so the team had to separately develop and execute a dedicated procedure, which took extra time.
The last unauthorized transfer was 2,961.9 ETH, completed on-chain at 23:56 UTC. This transaction had previously been broadcast and had remained pending confirmation. Only at 00:10 UTC on October 30 did Binance send a new authorization from hot wallet No. 14 to the zero address, clearing the EIP-7702 delegation code. From the first outgoing transfer to the completion of the revocation, nearly four hours elapsed.
These wallets belonged to different chains, different key types, and different signing mechanisms, yet all produced valid signatures for the attacker within half an hour. The most likely explanation is that the attacker gained the ability to make Binance’s hot wallet signing system initiate transactions across chains. The report also noted that the 50 pre-signed authorizations suggest that access may have been time-limited, or that signing had to be requested through a certain system.
Freezing, Money Laundering, and the Remaining 2.4 Billion
Stablecoin issuers reacted quickly. Within 37 minutes after 20:01 UTC, Tether froze 971.1 million USDT in the main receiving wallet. It then froze 205 million in two attacker wallets on Ethereum, 378.7 million in two wallets on Tron, and 8.4 million on Avalanche. Circle froze 823 million USDC at 21:04 UTC. Ripple froze 40.5 million RLUSD, and World Liberty Financial froze 27.8 million USD1. The Arbitrum Security Council used emergency powers to force-transfer 8,426 ETH and 74.6 million ARB from the attacker wallets.
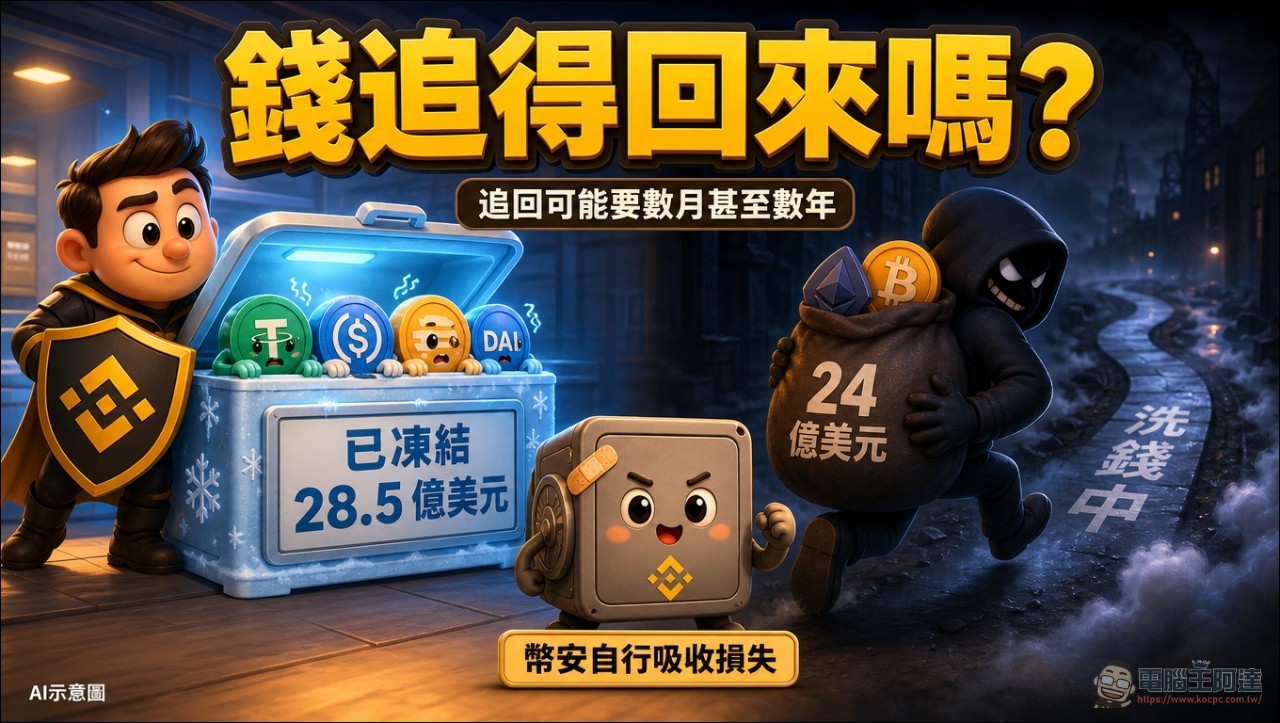
Binance’s November 3 report said it had cumulatively frozen or intercepted about $2.85 billion. But attackers are simultaneously running money laundering. TRM Labs recorded about $325 million USDT sold to professional market makers through intent-based contracts such as UniswapX, in exchange for about 122,300 ETH. Based on ETH’s market price at the time of about $2,300 to $2,350, these trades were priced near $2,650, a discount of more than 10%. Another wallet deposited $60 million USDT into Aave and borrowed about 19,760 ETH.
Ultimately, the attacker held more than 420,000 ETH and 18,270 BTC, about US$2.4 billion, assets that no issuer can freeze. The next stage is expected to involve cross-chain bridges, exchange services, and over-the-counter dealers. Binance co-CEO Richard Teng once said in an interview that Ripple’s assistance prevented the movement of about US$200 million in funds.
Compensation Progress and User Impact
Binance’s first response was to bear all losses. The October 30 update said the company had secured more than 100% of the required funds; by October 31, 98% of the affected token assets had been replenished and could be verified on the Proof of Reserves page. Binance used the Secure Asset Fund for Users (SAFU), part of the futures insurance fund, and the company’s financial reserves. The November 1 update mentioned that ten tokens—BTC, ETH, USDT, BNB, SOL, USDC, XRP, USD1, RLUSD, and ZEC—had reached 100% full backing, and the remaining unreplenished 10% were tokens outside its top ten with lower liquidity, so procurement would take more time.
On November 3, Binance listed the completed work: rebuilding the affected wallet systems in a new environment, rebuilding the affected internal AI tools and access permissions, replacing affected devices, disabling the credentials and tokens of the engineers involved, completing enhanced cybersecurity scans of all employee devices, and strengthening risk controls for wallet services and AI behavioral anomaly detection. Follow-up actions include hiring an independent third-party cybersecurity firm for a comprehensive review, increasing investment in AI detection and endpoint protection, and working with the industry to establish a cybersecurity research fund.
For users, the most direct impact was the suspension of withdrawals. Withdrawal services were paused after the incident and did not resume in stages until Sunday, October 31. Binance said its own wallet was affected, and user funds themselves were safe.BBC Citing a Binance spokesperson, net outflows after services resumed were about $4.72 billion, a limited proportion relative to total assets of about $157 billion. Binance’s U.S. affiliate said it was unaffected.
As for whether the money can actually be recovered, Ari Redbord, head of policy at TRM Labs, says freezing is a technical action, while recovery requires legal proceedings. Stablecoins, because issuers control the token contract, can be frozen, burned, and reissued, making them the easiest category to recover; Bitcoin and Ethereum have no direct channel for an issuer to freeze them, so recovery depends on tracing the flow of funds and waiting until they enter an exchange or other centralized platform that cooperates with the investigation, at which point there is a chance to intercept them. Eric Jardine, research director at Chainalysis, says there is no standard recovery timeline; technical freezing may happen quickly, while actual return may take months or even years.
Conclusion
Looking at these four months separately, this was a textbook compound attack combining supply chain and social engineering. The fake Homebrew in June allowed the attacker to map out the personnel on the Binance wallet team; the fake interview in September got him his first computer; the internal AI tool on October 20 became a springboard for lateral movement; and the signing service permissions on October 29 opened the door to withdrawals. Every step landed in a gap someone else had failed to defend.
The $6.34 billion figure is indeed staggering, but what is more worth noting is how it happened. Binance’s endpoint protection blocked the June incident, and the security team blocked 57 suspected North Korea-related attacks in 2026. Those defenses all worked. What failed was the act of “Engineer B downloading an assignment near the end of an interview” and the habit of “Engineer A keeping a container deployment token on their computer.”
TRM Labs’ advice to exchanges and compliance teams is straightforward: signing policies should reject unexpected EIP-7702 authorizations, and a single request for a large number of authorizations across multiple transaction counts should be treated as an indicator of compromise; signing infrastructure and approval paths should be isolated by chain and wallet tier, because in this case a single actor obtained valid signatures on ten chains within a few hours.
As for the money, Binance has promised to absorb the losses itself, and user funds are unaffected. But between the frozen $2.85 billion and the $2.4 billion in the attacker’s hands, no issuer can intercept the $2.4 billion in ETH and BTC. Jardine said there is no timetable for recovery; it could take months or even years. Getting this $6.3 billion back to where it belongs may take longer than finding the hackers.
Source: KOCPC Chinese