
The day before yesterday, the PHP2Shell vulnerability affected almost all PHP websites and caused many government and large enterprise websites to go offline to ride out the storm. The day after the news broke, the PHP team immediately released four versions at once, patching two vulnerabilities numbered CVE-2026-109618 and CVE-2026-109619. However, some small and medium-sized enterprises without maintenance capabilities may even have difficulty updating PHP. Trend Micro’s TrendLife observed this wave of impact and today launched a new service, “TrendLife PHP“Vulnerability First Aid Kit,” designed for small and medium-sized enterprises before they complete the underlying remediation,
Two vulnerabilities rated 9.2, with patches released the same day
The root causes of both vulnerabilities, CVE-2026-109618 and CVE-2026-109619, lie in memory management. According to the National Institute of Standards and Technology’s vulnerability database, the issue in CVE-2026-109618 is that when PHP uses longjmp() to handle out-of-memory errors, some execution contexts are not handled correctly, leaving request memory in an uninitialized state before allocation, and subsequent request cleanup routines may read from or branch on this memory. CVE-2026-109619 involves global state that, after being reset, may still point to freed request memory, and subsequent requests may read or base decisions on it before the state is fully initialized. Both can reliably trigger remote code execution.
The vulnerability types listed in the official PHP security advisory are exactly the same: use after free (CWE-416), improper handling of exceptional conditions (CWE-755), access of uninitialized pointer (CWE-824), improperly controlled sequential memory allocation (CWE-1325), and incorrect initialization of resource (CWE-1419). The CVSS 4.0 vector string is AV:N/AC:H/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H; an attack requires no privileges and can be attempted as long as the target is network-reachable.
The patched versions were all released on the same day, and the announcements for all four branches stated that this was a security release:
- PHP 8.5.12、8.4.27、8.3.36、8.2.35, all released on October 22.
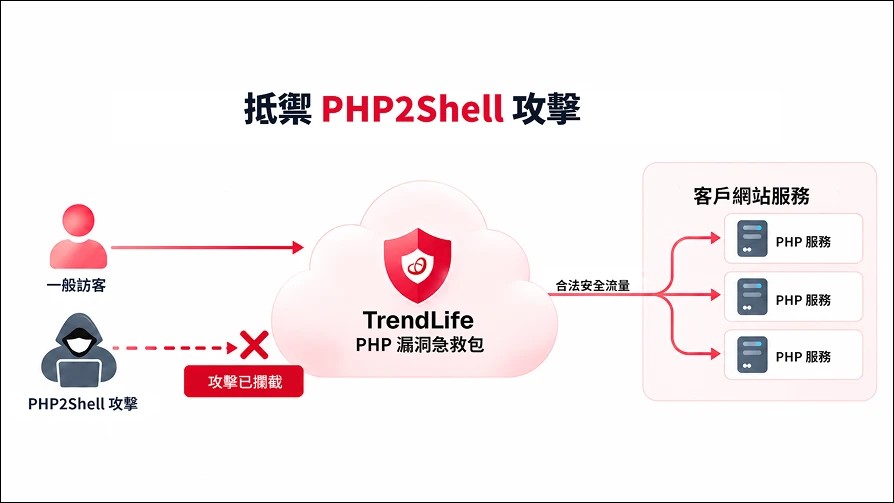
TrendLife PHPThe vulnerability emergency kit temporarily blocks threats in front of the website.
TrendLife PHP Vulnerability Emergency Kit adopts a proxy architecture and is deployed in front of websites as the first line of defense for external traffic, intercepting malicious requests from bad actors before they reach the server and helping prevent known PHP attack methods such as PHP2Shell. Its protection rules are specifically optimized for PHP, WordPress, and Laravel websites and include the following features:
- Managed protection: Simple to set up and managed and maintained by TrendLife, with no need to tune the rules yourself.
- Multi-domain protectionA single service can protect multiple domains, with up to 10 hostnames under the same domain.
- Includes a free SSL certificateAutomatically issued and renewed at no extra cost (you can also use your own certificates).
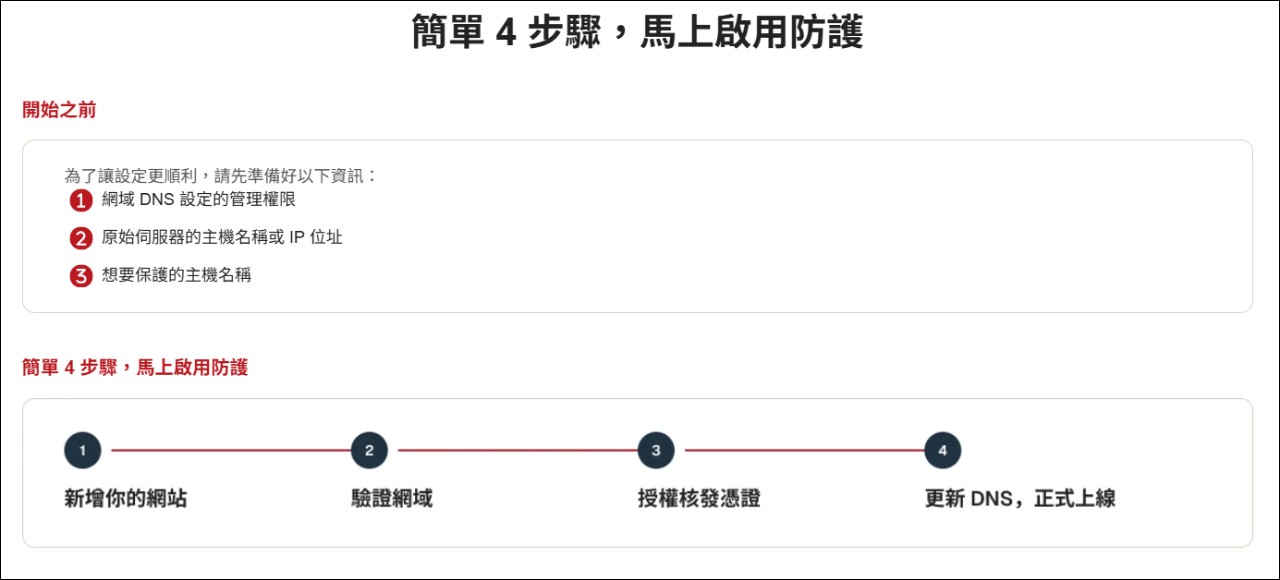
- 30Get online quickly in minutes with 3 steps.Add a website, verify domain ownership, and enable protection; setup takes about 30 minutes.
CEO Chen Yi-hua: Engineers worked through the night.
Trend Micro CEO and co-founder Eva Chen said: “PHPThe vulnerability affects major and medium-sized … worldwide,
With immediate effect7days free
TrendLife PHPThe Vulnerability First Aid Kit is now available free of charge to small and medium-sized enterprises, effective immediately.7Day,
Source: TrendLife PHP Vulnerability Emergency Kit Product Page
Source: KOCPC Chinese